Cyber Resilience Act · Annex VII
The CRA technical file, drafted: eleven documents
The technical documentation Article 31 and Annex VII require of a manufacturer, as eleven documents for one product, delivered as PDF and DOCX, generic placeholders where your product goes.
€5,000
Documents by email within minutes; add them to a free workspace whenever you like.
excl. VAT · one payment · invoice from Paddle · no account
The 11 documents
Every document by name, one line on what it settles, and the point of the Regulation it satisfies.
1 · Article 3 and Annex III
Scope and classification determination
Whether the product is in scope, and its class under Annex III, with the reasoning.
2 · Annex VII point 1, Annex II
General description and user information
What the product is, what it does and what the user is told, per Annex II.
3 · Annex VII point 3, Annex I Part I
Cybersecurity risk assessment
The Article 13 risk assessment against every Annex I Part I requirement.
4 · Annex VII point 2, Annex I Part II
Vulnerability handling process
How vulnerabilities are found, fixed and communicated, per Annex I Part II.
5 · Annex VII point 4, Article 13(8)
Support period determination
How long security updates are provided and why, per Article 13(8).
6 · Annex VII points 5 and 6
Standards applied and test evidence
Which standards and specifications apply and the evidence that tests were run.
7 · Annex VII point 7, Annex V
EU declaration of conformity (draft)
The declaration of conformity, ready for the signature, per Annex V.
8 · Annex I Part II points 5 and 6
Coordinated vulnerability disclosure policy
The coordinated vulnerability disclosure policy the Regulation requires to be published.
9 · Annex I Part II points 2, 7 and 8, Article 13(8)
Security updates and support statement
What updates are provided, how, for how long, and where the user reads it.
10 · Annex I Part II point 1
Software bill of materials procedure
How the software bill of materials is produced, in which format, and kept current.
11 · Article 14, Article 71(2)
Article 14 reporting procedure
Who reports what to ENISA and the CSIRT, and the 24-hour, 72-hour and 14-day steps.
A sample page
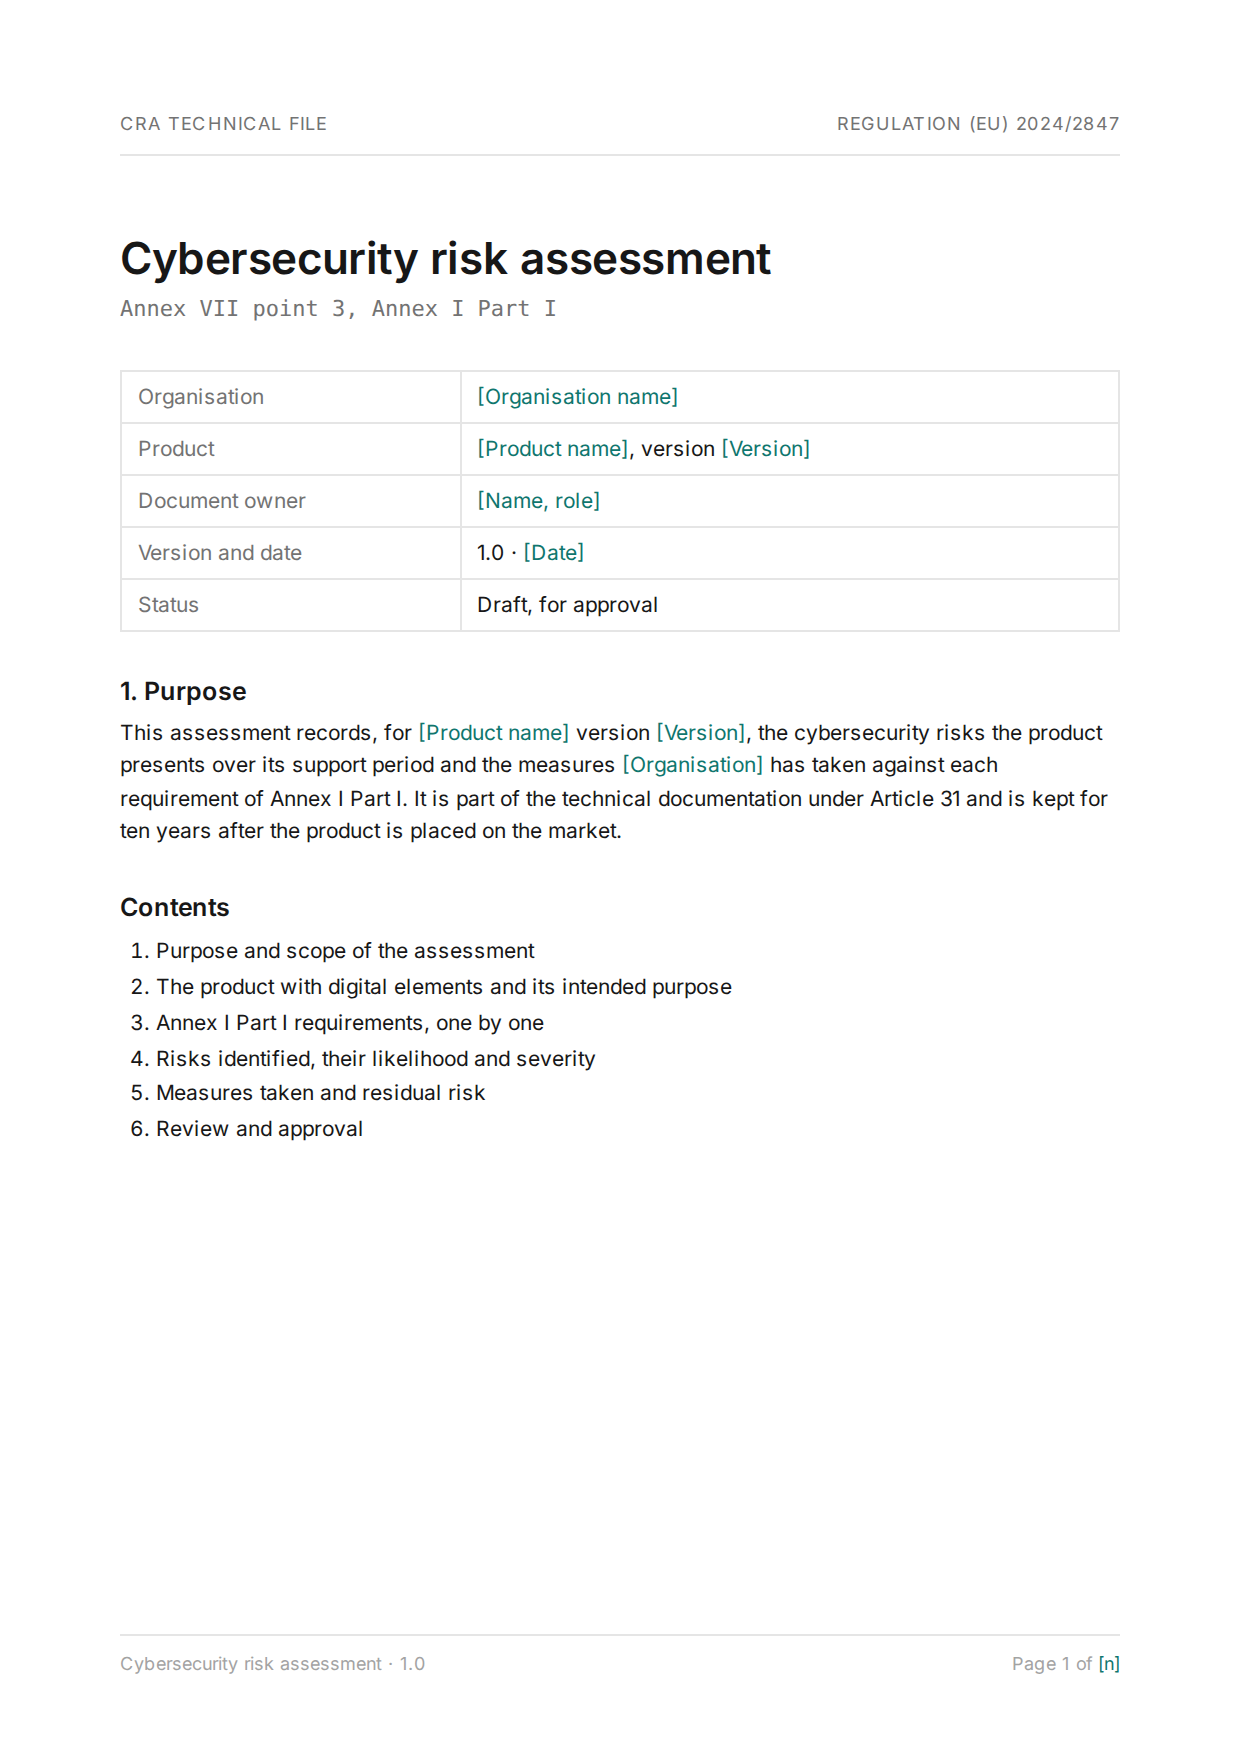
The first page of the Cybersecurity risk assessment, as it arrives: PDF and DOCX, the generic placeholders in square brackets are what your workspace fills in.
Who it is for
- A manufacturer of software or a connected product placed on the EU market, with a technical file to show from 11 December 2027.
- A team that would rather start from a complete, structured set than from the Regulation's text.
- A consultancy drafting the file for a client, one set per product.
Who it is not for
- A product outside the Regulation's scope; the scope check on the CRA hub is free.
- An importer or distributor: the importer and distributor pack is the one with your duties.
- A team that needs the file kept current across releases: that is the workspace's job, not a file's.
How delivery works
1. Pay
Paddle takes the payment in the overlay on this page and issues the invoice, VAT handled for your country.
2. Receive
Within minutes an email carries a link, good for seven days, to the set as PDF and DOCX.
3. Use, or claim
Edit the DOCX yourself, or create a free workspace with the same email: the purchase attaches to it and the documents are drafted again from your own product record.
In a workspace
A workspace created, or an owner signing in, with the buyer's address claims the purchase once. The same 11 documents are then drafted from the product you register, kept current as the record changes, and exported with the audit trail. The trial is 14 days, no card.
Regulation references
Every document names the article or annex point it satisfies; the Official Journal text is the source, read in English.
- Article 3 and Annex III
- Annex VII point 1, Annex II
- Annex VII point 3, Annex I Part I
- Annex VII point 2, Annex I Part II
- Annex VII point 4, Article 13(8)
- Annex VII points 5 and 6
- Annex VII point 7, Annex V
- Annex I Part II points 5 and 6
- Annex I Part II points 2, 7 and 8, Article 13(8)
- Annex I Part II point 1
- Article 14, Article 71(2)
The terms
- One payment; the invoice comes from Paddle, our merchant of record, with VAT for your country.
- The documents are yours to edit and keep; a link that has expired is re-sent on request.
- Cancellation and refund terms are on the cancellation page. Cancellation and refund
Questions
- Is this the full technical documentation Annex VII asks for?
- It is the structure and the drafted text of every Annex VII point; the product-specific facts, test results and the SBOM are yours to fill in, and the placeholders show where.
- Do I need an account to buy it?
- No. Paddle takes the payment on this page and the documents arrive by email. A free workspace can claim the purchase later if you want them drafted from your own product record.
- Which product classes does it cover?
- Default products under self-assessment (Module A). An important or critical product needs the same file plus a conformity route the documents name; the scope determination in the pack decides which.
- In which language are the documents?
- English, the language every notified body and market surveillance authority accepts for the file; the page and the support are in yours.
- What does the workspace add?
- The same eleven documents drafted from the product you register, the Article 14 clocks, the notifications drafted when a vulnerability is exploited, and an export with the audit trail.
The other path
€249 a month runs the same file live: register the product, the workspace drafts every document from its record, keeps the clocks and stays current.
Start free, 14 days, no card